

[Aug-2026] Updated Cisco 350-101 Dumps – PDF & Online Engine
350-101.pdf - Questions Answers PDF Sample Questions Reliable
NEW QUESTION # 19
A wireless engineer must manage a scheduled maintenance window for a mesh network within a network that uses Cisco Catalyst Center as the primary monitoring solution. The engineer must coordinate downtime and verify that all services resume as intended after planned tasks are complete. How does the engineer avoid unnecessary alerting in Cisco Catalyst Center throughout the maintenance window?
- A. Schedule maintenance for the devices
- B. Disable telemetry on the WLC
- C. Enable device suppression
- D. Use SWIM for firmware updates on mesh APs
Answer: C
Explanation:
In Cisco Catalyst Center,device suppressionis the recommended method to prevent unnecessary alerts during planned maintenance windows. By enabling device suppression, the system temporarily suspends monitoring and alert generation for the selected devices while allowing telemetry collection to continue. This ensures that maintenance operations, such as firmware upgrades, configuration changes, or physical mesh AP servicing, do not trigger false-positive alarms. Once the maintenance window concludes, alerts resume automatically, and the engineer can verify that all services are operational and that no critical issues were overlooked.
Disabling telemetry on the WLC (option A) is not advised because it prevents visibility into device health and network performance, potentially causing gaps in monitoring data. Using SWIM (option B) is relevant for automated firmware updates but does not inherently suppress alerts during maintenance. Scheduling maintenance for devices (option C) without enabling device suppression may still generate alerts if the monitoring system detects device reboots or temporary unreachability.
Cisco wireless operational guides specifically highlightdevice suppression as the key tool for managing alerting behaviorduring planned events in mesh or enterprise WLAN deployments, providing a controlled approach to maintenance with minimal disruption to monitoring accuracy. Reference topic:Wireless Monitoring and Management - Catalyst Center, device suppression, scheduled maintenance, and alert control.
NEW QUESTION # 20
An engineer troubleshooting AP join failures notices DTLS negotiation errors between APs and the controller. Which issue is MOST likely responsible?
- A. Time synchronization or certificate validation failure
- B. Incorrect RF profile
- C. Excessive multicast traffic
- D. Invalid DHCP Option 43 subnet mask
Answer: A
Explanation:
DTLS relies on valid certificates and accurate time synchronization. Significant clock mismatches or certificate validation problems frequently prevent secure CAPWAP tunnels from forming between APs and controllers. RF profiles and multicast conditions generally do not affect DTLS establishment directly.
NEW QUESTION # 21
Refer to the exhibit. A client authenticates via 802.1X against an ISE server that is configured to return a specific VLAN ID (VLAN 100) via an attribute value pair. However, the administrator notices that the client is placed in the wrong VLAN (VLAN 50). What must the administrator implement to resolve the issue?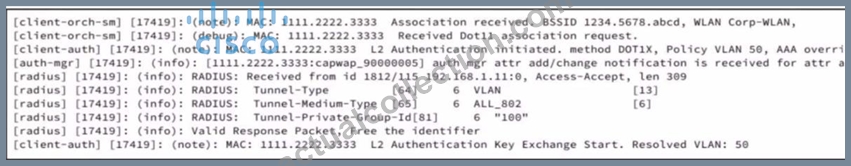
- A. Configure the policy profile to allow ISE to override the VLAN.
- B. Configure VLAN 100 on the trunk ports of the WLC.
- C. Configure AAA VLAN enable on the WLAN.
- D. Configure VLAN 100 as an SVI on the WLC.
Answer: A
Explanation:
In this scenario, the client is placed in the wrong VLAN (VLAN 50) even though the ISE server is configured to assign VLAN 100. The key part of the issue is that the VLAN assignment returned by ISE is not being applied correctly.
Option A: "Configure the policy profile to allow ISE to override the VLAN." This is the correct answer. The policy profile on the Wireless LAN Controller (WLC) should be configured to allow the ISE server's VLAN assignment to override the locally configured VLAN settings on the WLC.
Without this, the WLC might default to its pre-configured VLAN (VLAN 50) instead of the VLAN assigned by ISE (VLAN 100).
NEW QUESTION # 22
What is a benefit of network adaptability in terms of improved operational outcomes when using AI-RRM in Cisco Catalyst Center?
- A. reduction of co-channel interference
- B. categorization of users by authentication type
- C. transmission of regular software update schedules
- D. provisioning of static device addresses
Answer: A
Explanation:
The correct answer isreduction of co-channel interference. AI-RRM in Cisco Catalyst Center is designed for RF optimization, not IP addressing, software scheduling, or user identity classification. Cisco describes AI- enhanced RRM as applying artificial intelligence and machine learning to optimize RF environments and automate/adapt RF parameter tuning for Cisco wireless networks. This is directly tied to operational RF outcomes such as improved channel planning, transmit power behavior, channel width decisions, and better spectrum utilization.
Co-channel interference occurs when multiple AP radios operate on the same channel within hearing range, forcing devices to share airtime and increasing contention. AI-RRM uses telemetry, analytics, and learned RF behavior to recommend or apply more optimal RF configurations. Cisco specifically states that AI-enhanced RRM optimization can produce improvements such as up to a40 percent reduction in co-channel interferenceand SNR gains for wireless clients. Cisco's AI-RRM deployment guidance also identifies AP radio distribution and utilization analysis as critical for minimizing co-channel interference and optimizing wireless performance.
Therefore, option B is the only operational outcome aligned with AI-RRM's purpose. Reference topic:
Automation and AI - Cisco Catalyst Center AI-RRM, RF analytics, RRM automation, channel optimization, and wireless AIOps.
NEW QUESTION # 23
What is a characteristic of 20 MHz channel width in a wireless network?
- A. Narrowest channel width in the 2.4 GHz band
- B. Supports automatic client reassociation
- C. Higher throughput than wider channels
- D. Increases authentication handoff frequency
Answer: A
Explanation:
In wireless networks, the 20 MHz channel width is the standard and narrowest channel allocation in the 2.4 GHz frequency band. Using narrower channels reduces adjacent-channel interference and allows for better coexistence in high-density environments, which is particularly important in the crowded 2.4 GHz spectrum. A 20 MHz channel uses less RF bandwidth than 40 MHz or 80 MHz channels, providing more non-overlapping channels (channels 1, 6, and 11 in 2.4 GHz) to reduce co- channel interference.
NEW QUESTION # 24
What is the main benefit of using AI Enhanced RRM on the Cisco Catalyst 9800 wireless controller?
- A. It is an automatic tuning tool that is used to adjust RF parameters based on static thresholds.
- B. It focuses on increasing the transmit power of access points to maximize coverage regardless of interference.
- C. It disables dynamic channel assignment and power control to maintain a fixed wireless environment for stability.
- D. It uses machine learning and cloud analytics to proactively optimize RF parameters.
Answer: D
Explanation:
AI Enhanced RRM is not a static-threshold tuning feature and it is not designed to simply raise AP transmit power. Cisco defines AI Enhanced RRM as a radio resource management technology that applies artificial intelligence and machine learning to optimize RF environments, uses distributed data collection from Cisco wireless controllers with cloud-based analytics, and automates adaptive RF parameter tuning for Cisco wireless networks.
The operational model is telemetry-driven. RF telemetry is collected from APs by the Catalyst 9800 WLC, sent through Cisco Catalyst Center to the Cisco AI Analytics Cloud, analyzed by RRM algorithms, and then configuration-change information is returned through Catalyst Center toward the managed wireless infrastructure. Cisco's AI-Enhanced RRM deployment guide further identifies DCA, TPC, FRA, and DBS as examples of optimizations performed, meaning the feature enhances dynamic RF control rather than disabling it.
Therefore, option D is the only correct answer. Options A, B, and C describe either legacy/static behavior, harmful power-only logic, or a fixed RF design model that contradicts Cisco AI Enhanced RRM. Reference topics:Automation and AI - AI/ML-driven RF optimization, Catalyst Center assurance, RRM telemetry, DCA, TPC, FRA, and DBS.
NEW QUESTION # 25
Refer to the exhibit. A network administrator is working on a WLC to enable user access for employee tablets using PEAP-MSCHAPv2 with a RADIUS backend. The administrator verifies the external authentication configuration and plans to test network connectivity. Which code snippet must be added to the configuration for the WLC to support authentication with an external server?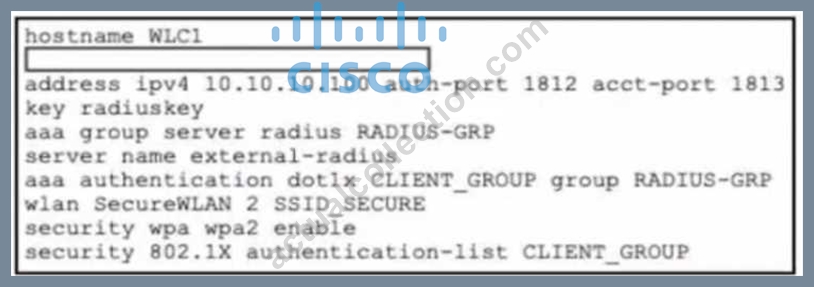
- A. radius server external-radius
- B. radius server RADIUS-GRP
- C. external-radius RADIUS-GRP
- D. external-radius aaa server
Answer: A
Explanation:
The missing command is radius server external-radius. On a Catalyst 9800 WLC, the external RADIUS server object must be declared first with radius server <server-name>. The following lines, address ipv4 10.10.10.100 auth-port 1812 acct-port 1813 and key radiuskey, are subcommands entered under that RADIUS server configuration mode. Cisco's Catalyst 9800
802.1X configuration workflow starts by declaring the RADIUS server, then adding it to a RADIUS server group, then creating the authentication method list, and finally mapping that list to the WLAN. Cisco's configuration guide example uses the same IOS XE structure: radius server
<name>, followed by address ipv4 ... auth- port 1812 acct-port 1813 and key ....
The server group later references server name external-radius, so the RADIUS server object must be named external-radius exactly. Option C would incorrectly create a server named RADIUS-GRP, which is already the AAA server group name, not the RADIUS server object.
Options B and D are invalid IOS XE syntax. PEAP-MSCHAPv2 itself is handled through the
802.1X/EAP exchange with the RADIUS server; the WLC acts as the authenticator and forwards authentication requests through the configured AAA method list.
NEW QUESTION # 26
Refer to the exhibit.
import requests
import json
API_ENDPOINT_URL = "https://your-network-platform.com/api/v1/wireless-clients" AUTH_TOKEN = "YOUR_SECRET_AUTH_TOKEN" headers = {
"Content-Type": "application/json",
"Authorization": f"Bearer {AUTH_TOKEN}"
}
print("Requesting wireless client data from the API...")
try:
response = requests.get(API_ENDPOINT_URL, headers=headers, timeout=10)
response.raise_for_status()
client_data = response.json()
print("Successfully retrieved and parsed data.\n")
print("--- Wireless Client Details ---")
if isinstance(client_data, list) and client_data:
for client in client_data:
mac_address = client.get("macAddress", "N/A")
ip_address = client.get("ipAddress", "N/A")
ssid = client.get("ssid", "N/A")
print(f"Client MAC: {mac_address}, IP: {ip_address}, SSID: {ssid}")
else:
print("No client data found or the data format is unexpected.")
except requests.exceptions.RequestException as e:
print(f"An error occurred during the API request: {e}")
except json.JSONDecodeError:
print("Failed to parse the API response. It may not be valid JSON.")
A network engineer is investigating how json library is used within a Python script designed to access response content from a Cisco wireless network API endpoint. The engineer wants to better understand how the script uses these elements to process device information. Which approach does the script use to achieve its data extraction goal?
- A. dumps function
- B. split method
- C. loads function
- D. to_dict method
Answer: C
Explanation:
The correct answer isloads functionbecause the script's extraction goal depends on deserializing JSON response data into native Python objects that can be indexed and queried. Cisco Catalyst Center APIs use REST methods and require payloads to and from the REST interface to be in JSON format, including wireless and client information workflows. In the exhibit, the call client_data = response.json() decodes the HTTP response body into Python data structures. That behavior is functionally aligned with json.loads(): JSON objects become Python dictionaries, JSON arrays become Python lists, and strings/numbers become Python- native equivalents. Python's JSON decoder documentation shows this JSON-to-Python conversion model explicitly, including object-to-dict and array-to-list mappings.
After decoding, the script validates that client_data is a list, iterates through each client record, and uses dictionary .get() to extract macAddress, ipAddress, and ssid. The Requests library documents that Response.
json() decodes a JSON response body as a Python object and may return a dictionary or list, which is exactly what the script consumes. dumps performs the opposite operation, split only tokenizes strings, and to_dict is not used here. Reference topic:Automation and AI - REST APIs, JSON parsing, wireless client telemetry extraction, and Python-based network automation.
NEW QUESTION # 27
What defines device sensitivity in a wireless environment?
- A. capability to process the signal
- B. implementation of key refresh schedules
- C. synchronization of beacon intervals
- D. detection of redundant gateways
Answer: A
Explanation:
Device sensitivity in a wireless environment refers to receiver sensitivity: the minimum RF signal level a client or AP radio must receive to successfully detect, demodulate, and decode a transmission. Cisco defines receiver sensitivity as the minimum signal power level, expressed in dBm or mW, required for a receiver to accurately decode a given signal. Cisco RF design guidance further states that sensitivity indicates the lowest received power before the receiver considers the signal unintelligible.
Therefore, option A is correct because sensitivity is fundamentally about the radio's capability to process a received signal at low power levels. A more sensitive receiver can decode weaker frames, improving effective coverage and receive performance, provided the signal-to-noise ratio and interference conditions remain acceptable. Cisco also notes that individual device sensitivity determines how well a device can hear and demodulate RF energy, which directly affects contention behavior and WLAN performance in dense environments. Redundant gateways, beacon interval synchronization, and key refresh schedules are Layer 3 availability, 802.11 timing, and security-key management topics; they do not define RF receiver sensitivity.
Reference topics:RF Fundamentals - receiver sensitivity, RSSI, dBm, SNR, demodulation, and WLAN coverage behavior.
NEW QUESTION # 28
Refer to the exhibit. A retail business is deploying guest wireless across its remote branch locations. Each branch uses FlexConnect APs in local switching mode, and the central wireless LAN controller is configured with an ACL named CWA_REDIRECT. Cisco ISE is configured to return this ACL during the authentication process for central web authentication (CWA). However, when clients attempt to connect to the guest wireless LAN, they are added to the exclusion list. Which configuration step resolves the connectivity issue?
- A. Change the ACL to include the ISE IP address.
- B. Map the ACL CWA_REDIRECT to the flex profile as a policy ACL.
- C. Include the ACL CWA_REDIRECT in the AP-Join profile.
- D. Add the ACL CWA_REDIRECT to the policy profile.
Answer: B
Explanation:
The failure is caused by the redirect ACL not being available where enforcement occurs. In FlexConnect local switching, client data-plane handling occurs on the AP, so the CWA redirect ACL cannot exist only as a controller ACL or only as a policy-profile reference. Cisco states that the redirect ACL is a punt ACL and that, for FlexConnect local switching, the ACL must be predefined on the AP because the AAA server returns only the ACL name, not the ACL definition.
The exhibit showsRedirect ACL failureandEXCLUDE_PUNT_ACL_FAIL, which aligns with an AP-side punt/redirect ACL application failure. Cisco's Catalyst 9800 CWA configuration specifically requires the redirect ACL definition to be sent through the FlexConnect profile; in the GUI this is done under the Flex ProfilePolicy ACLtab by adding the ACL, enabling central web authentication, and applying the change. The equivalent CLI iswireless profile flex < profile > followed byacl-policy < acl-name > andcentral-webauth, after which the AP uses the ACL for client redirection. AP-Join profiles do not carry client redirect ACL policy, and adding the ACL only to the policy profile does not push it to FlexConnect APs for local switching.
Reference topics:FlexConnect local switching, CWA redirect ACLs, Catalyst 9800 policy ACLs, and ISE URL-redirect authorization.
NEW QUESTION # 29
Refer to the exhibit.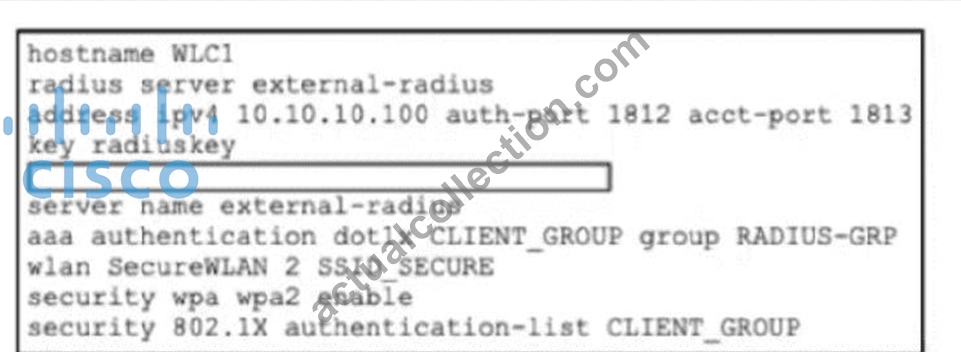
A network administrator is working on a WLC to enable user access for contractor desktops using WPA2- Enterprise using EAP-TTLS. The administrator verified the external authentication configuration and now must test network connectivity. Which code snippet must be added to the box in the code to complete the configuration on the WLC that supports authentication with an external server?
- A. aaa group server aaa RADIUS-GRP
- B. aaa server group server radius RADIUS-GRP
- C. aaa group server radius RADIUS-GRP
- D. aaa server group server radius RADIUS-GRP
Answer: C
Explanation:
The missing command must create the RADIUS server group context before the existingserver name external- radiuscommand can bind the defined RADIUS server into that group. Cisco's Catalyst 9800 802.1X configuration workflow shows the exact CLI sequence: define the RADIUS server, then enteraaa group server radius < radius-grp-name > , then addserver name < radius-server-name > . The Catalyst 9800 configuration guide likewise states that the RADIUS server-group identification is created withaaa group server radius server-group, followed by the server name assignment.
In this exhibit,external-radiusis already declared underradius server, andaaa authentication dot1x CLIENT_GROUP group RADIUS-GRPalready points the 802.1X method list to the server group namedRADIUS-GRP. Therefore, the box must containaaa group server radius RADIUS-GRPso thatserver name external-radiusis syntactically valid and functionally associates the external server with the group. Cisco also identifies dot1x authentication lists as the AAA method type used for 802.1X SSIDs, with "group" directing authentication to an external RADIUS server. Reference topics:Client Connectivity Configuration
- WPA2-Enterprise, 802.1X/EAP, AAA method lists, RADIUS server groups, and Catalyst 9800 WLAN security
NEW QUESTION # 30
Refer to the exhibit. A network administrator is working on a WLC to enable user access for contractor desktops using WPA2-Enterprise using EAP-TTLS. The administrator verified the external authentication configuration and now must test network connectivity. Which code snippet must be added to the box in the code to complete the configuration on the WLC that supports authentication with an external server?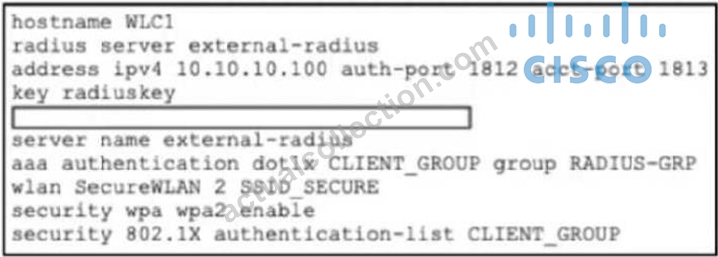
- A. aaa group server aaa RADIUS-GRP
- B. aaa server group server radius RADIUS-GRP
- C. aaa group server radius RADIUS-GRP
- D. aaa server group server radius RADIUS-GRP
Answer: C
Explanation:
The missing command must create the RADIUS server group context before the existing server name external-radius command can bind the defined RADIUS server into that group. Cisco's Catalyst 9800 802.1X configuration workflow shows the exact CLI sequence: define the RADIUS server, then enter aaa group server radius <radius-grp-name>, then add server name <radius- server-name>. The Catalyst 9800 configuration guide likewise states that the RADIUS server- group identification is created with aaa group server radius server-group, followed by the server name assignment.
In this exhibit, external-radius is already declared under radius server, and aaa authentication dot1x CLIENT_GROUP group RADIUS-GRP already points the 802.1X method list to the server group named RADIUS-GRP. Therefore, the box must contain aaa group server radius RADIUS- GRP so that server name external-radius is syntactically valid and functionally associates the external server with the group. Cisco also identifies dot1x authentication lists as the AAA method type used for 802.1X SSIDs, with "group" directing authentication to an external RADIUS server.
NEW QUESTION # 31
How does MIMO operate during wireless transmission?
- A. It shares a single connection among endpoints for coverage expansion.
- B. It applies frequency hopping to prevent crosstalk.
- C. It uses multiple radio paths to increase throughput and reliability.
- D. It limits data paths to a single antenna for error reduction.
Answer: C
Explanation:
MIMO, or Multiple-Input Multiple-Output, is a core 802.11n and later wireless technology that uses multiple transmit and receive radio chains and antennas to improve wireless performance. Cisco's Wireless RF Reference Guide explains that IEEE 802.11n introduced MIMO, replacing the older single-radio SISO model with multiple radios, each using its own antenna, to increase data rates and improve reception in multipath environments. Cisco also notes that weak or distorted multipath signals can be received by more than one radio and reconstructed, improving decode quality and reliability.
This directly supports option A: MIMO exploits multiple RF paths rather than treating multipath as purely destructive. Depending on implementation, MIMO can use spatial diversity, maximal ratio combining, and spatial streams to increase throughput, improve signal-to-noise ratio, reduce retries, and make more efficient use of airtime. Cisco describes spatial stream notation such as 4x4:4 as four transmitters, four receivers, and four spatial streams. Option B describes frequency hopping, not MIMO. Option C is not a MIMO function.
Option D is the opposite of MIMO because MIMO deliberately uses multiple antennas and radio paths.
Reference topics:802.11 Technology Fundamentals - MIMO, spatial streams, multipath, SISO versus MIMO, and 802.11n/ac/ax PHY enhancements.
NEW QUESTION # 32
Which Cisco Ultra-Reliable Wireless Backhaul process enables devices to establish a reliable connection with the next AP along their path before losing connectivity to the current one in a wireless network during roaming?
- A. Open roaming
- B. 802.11v high speed roaming
- C. Fast client handoff
- D. Make-before-break handover logic
Answer: D
Explanation:
The correct answer isMake-before-break handover logic. This is a key feature in Cisco's Ultra-Reliable Wireless Backhaul (URWB) process that allows devices to establish a connection to the next AP (Access Point) before disconnecting from the current AP. This seamless transition ensures that there is no disruption in the wireless connection as the client roams between APs, which is especially important in environments where consistent, low-latency connectivity is essential, such as in real-time applications (e.g., voice or video).
Option A (Open roaming)refers to a method of allowing devices to roam freely across networks, but it doesn't address the specific need for a seamless handover process.
Option B (Fast client handoff)refers to methods used to speed up the roaming process, but it doesn't specifically ensure that the next AP is connected before disconnecting from the current one.
Option C (802.11v high speed roaming)is an IEEE standard feature that helps optimize roaming behavior for fast-moving devices, butmake-before-break handover logicis the specific mechanism that allows for a seamless roaming experience.
Therefore,Make-before-break handover logic(Option D) is the correct answer as it directly addresses the need for devices to establish a reliable connection to the next AP during roaming before losing connectivity with the current one.
NEW QUESTION # 33
Refer to the exhibit. An engineer configured a static IP address on a LWAPP, but it is not reachable for management. The engineer configured the wrong gateway and must now change the default gateway to 172.16.100.1. Which CLI command must the engineer use?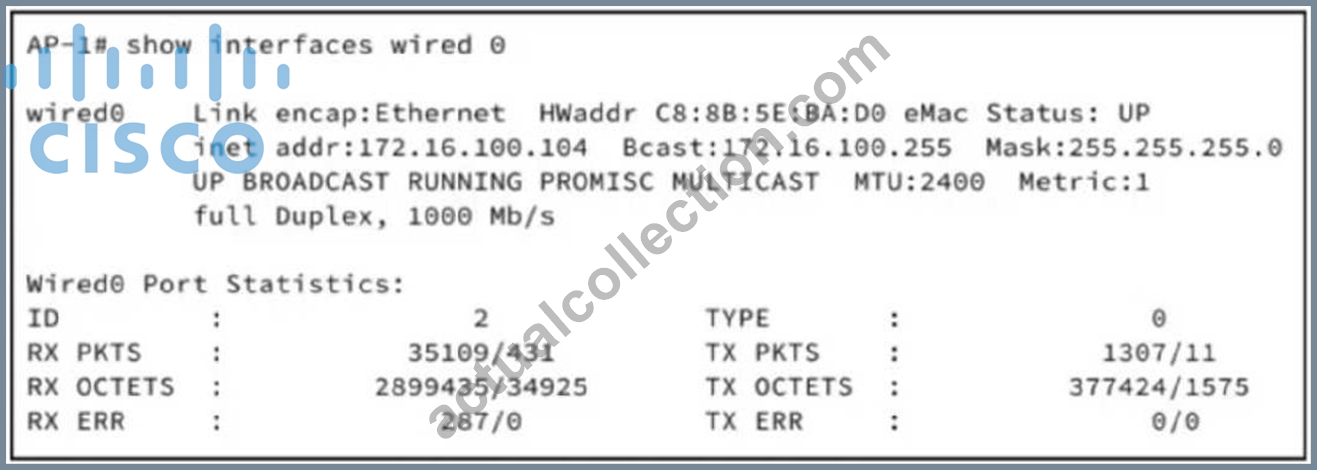
- A. capwap ap ip 172.16.100.104 255.255.255.0 172.16.100.1
- B. capwap ap ip 172.16.100.104 255.255.255.192 172.16.100.1
- C. capwap ap controller ip address 172.16.100.1
- D. capwap ap ip default-gateway 172.16.100.1
Answer: A
Explanation:
When deploying a Lightweight Access Point (LWAPP) in a Cisco wireless network, proper Layer
3 configuration is essential for management and connectivity to the Wireless LAN Controller (WLC). Each LWAPP requires a valid IP address, subnet mask, and default gateway to communicate beyond its local subnet. In the exhibit, the AP is assigned 172.16.100.104/24, but the previously configured gateway was incorrect, preventing communication with the WLC. Cisco IOS XE requires that the AP's IP interface be configured with the correct default gateway to route traffic properly. The correct syntax is capwap ap ip <AP-IP> <Subnet-Mask> <Default-Gateway>.
Option D matches the IP, subnet mask, and gateway for the given network, ensuring the AP can reach the WLC for LWAPP registration.
NEW QUESTION # 34
How does enabling webhook notifications enhance Cisco Meraki Wireless integration?
- A. lightweight way to subscribe to alerts
- B. isolated notification delivery
- C. predictable device discovery timing
- D. periodic manual firmware installations
Answer: A
Explanation:
Enabling webhook notifications in Cisco Meraki Wireless environments provides a lightweight, event-driven method for external systems to receive real-time alerts and status updates from the network. Webhooks eliminate the need for constant polling of the Meraki Dashboard API, allowing systems to automatically respond to events such as AP connectivity changes, client onboarding, SSID status, or anomalous traffic patterns. This approach reduces network and compute overhead compared to frequent API queries, ensuring that alerts are delivered efficiently and promptly.
By subscribing to webhooks, integrations can trigger automated workflows, such as incident tickets, push notifications, or AI-driven remediation actions, which enhances operational agility.
Unlike periodic polling or scheduled scripts, webhooks provide immediate and contextual data without manual intervention, making them ideal for automated monitoring, alerting, and analytics systems. Options B, C, and D are incorrect because webhook notifications do not control device discovery timing, do not isolate delivery beyond standard API security, and do not manage firmware installations manually.
Cisco's Meraki technical documentation emphasizes that webhooks are a lightweight, scalable, and automated mechanism for alerting and integrating third-party systems with the wireless network, supporting responsive operational intelligence and automation strategies.
NEW QUESTION # 35
A wireless deployment experiences intermittent client disconnections caused by excessive roaming sensitivity. Which client-side metric is MOST associated with roaming decisions?
- A. RSSI threshold
- B. RADIUS timeout
- C. Beacon interval only
- D. CAPWAP MTU
Answer: A
Explanation:
Clients primarily use RSSI thresholds and signal quality metrics to determine when roaming should occur. Aggressive roaming thresholds may trigger unnecessary AP transitions, resulting in instability. CAPWAP MTU and RADIUS timeout values do not directly influence roaming sensitivity decisions made by wireless clients.
NEW QUESTION # 36
An engineer deploys location tracking services for wireless clients and assets. Which Cisco solution enhances location accuracy using AP hardware capabilities?
- A. AVC
- B. Client exclusion
- C. Hyperlocation
- D. mDNS gateway
Answer: C
Explanation:
Cisco Hyperlocation uses specialized AP antenna arrays and advanced RF processing to improve wireless location accuracy for clients and assets. It supports more precise positioning compared to standard triangulation methods. AVC and mDNS provide application visibility and service discovery rather than location analytics.
NEW QUESTION # 37
A network administrator at a construction company manages a Cisco Catalyst 9800 Series Wireless Controller running Cisco IOS XE 17.x. The WLAN named XYZ-Conference is set up for a large event, but attendees report slow network performance due to misbehaving clients. To improve connectivity, the network administrator decides to change the client exclusion policy on the WLAN to temporarily block the misbehaving clients. The XYZ-Conference WLAN must enable a client exclusion policy with a timeout of
120 seconds for misbehaving clients. Which set of Cisco IOS XE commands must be used?
- A. wireless profile policy XYZ-Conferenceclient-exclusion 120
- B. wireless profile policy XYZ-ConferenceXYZ Conference exclude 120
- C. wireless profile policy XYZ-Conferenceexclusionlist timeout 120
- D. wireless profile policy XYZ-Conferencesecurity exclusion timeout 120
Answer: A
Explanation:
Client exclusion is a feature in Cisco Catalyst 9800 WLCs that allows the administrator to temporarily block clients exhibiting misbehavior, such as excessive retries, excessive bandwidth usage, or roaming issues. The IOS XE CLI command for enabling client exclusion in a WLAN policy isclient-exclusion < timeout > , where
< timeout > defines the duration (in seconds) the client is prevented from associating with the WLAN. Option D correctly usesclient-exclusion 120to block the misbehaving clients for 120 seconds. Option A (exclude 120) is not valid IOS XE syntax. Option B (exclusionlist timeout 120) is also incorrect as it refers to internal exclusion lists, not the WLAN policy applied to live clients. Option C (security exclusion timeout 120) is invalid and does not configure client exclusion at the WLAN policy level. Cisco Wireless Core Technologies emphasize using client exclusion policies during high-density events or temporary network congestion to ensure network fairness, protect overall WLAN performance, and maintain connectivity for well-behaving clients. Reference topics:Client Connectivity Configuration - Client exclusion, WLAN policy, misbehaving client mitigation, Cisco Catalyst 9800 IOS XE.
NEW QUESTION # 38
An enterprise requires certificate-based wireless authentication for employees. Which EAP method provides mutual authentication using client and server certificates?
- A. LEAP
- B. EAP-FAST
- C. EAP-TLS
- D. PEAP-MSCHAPv2
Answer: C
Explanation:
EAP-TLS uses certificates on both the client and authentication server, providing strong mutual authentication and eliminating password-based vulnerabilities. PEAP relies on passwords within a protected tunnel, while LEAP is deprecated due to known security weaknesses.
NEW QUESTION # 39
A medium-sized enterprise must provide wireless internet to visitors in their lobby using a Cisco
9800 WLC. The solution must meet these requirements:
- Ensure that guests cannot access the corporate LAN.
- Guests are redirected to a login page before browsing.
- The guest network must use a separate VLAN from internal users.
- Access must be limited to web browsing only.
- Guest access does not require any preshared keys or certificates.
Which two actions must be taken to achieve this solution? (Choose two.)
- A. Implement a policy profile with p2p blocking enabled and a guest VLAN.
- B. Apply a webauth WLAN with mDNS mode set to drop.
- C. Deploy a WLAN policy that points wireless users to a webauth parameter map.
- D. Create a WLAN that uses a web policy and points to a consent parameter map.
- E. Configure a policy profile that uses an external only ACL and guest VLAN.
Answer: C,D
Explanation:
To implement a guest Wi-Fi network on a Cisco 9800 WLC with the requirements mentioned, the solution must ensure that guests are isolated from the corporate LAN and are redirected to a login page before being able to access the internet. Additionally, access needs to be restricted to web browsing only, with no need for preshared keys or certificates.
Option A: "Create a WLAN that uses a web policy and points to a consent parameter map." This is necessary to enforce the login page and redirect users to a webauth page. By creating a WLAN with web policy, you ensure that users are redirected to a captive portal where they can accept the terms and conditions or login to the network. This solution also helps in segregating the guest network from the corporate network, as users are contained within their VLAN.
Option E: "Deploy a WLAN policy that points wireless users to a webauth parameter map." Web authentication (webauth) is an essential part of guest access. Deploying a WLAN policy with webauth ensures that users are directed to the login page (a webauth parameter map), allowing them to authenticate before browsing the internet.
NEW QUESTION # 40
A hotel wants to provide guests with wireless connectivity via a captive portal using a Cisco 9800 WLC. The solution must meet these requirements:
* Ensure that guests are redirected to a custom web page for login and after authentication must have only internet access.
* The guest SSID must not require a password and must be visible to all clients.
* Network segmentation between staff and guests is required at the VLAN level.
What must the IT team configure on the WLAN?
- A. open authentication with a local web server for the guest WLAN
- B. PSK WLAN with VLAN override and enable mDNS for guest users
- C. central web authentication and assign a policy with ACLs restricting access to internal networks
- D. central web authentication with WPA2-PSK security and a DNS ACL assigned to the WLAN profile
Answer: C
Explanation:
Central Web Authentication is the correct design for an open guest SSID that redirects users to a captive portal before allowing network access. Cisco describes CWA as a guest-redirection method where the redirect URL and redirect ACL are centrally controlled and communicated to the WLC through RADIUS, with the external authentication system handling the login workflow. On a Catalyst 9800 WLAN, Cisco's configuration flow for Central Web Authentication requires AAA/ACL configuration, including the AAA server list and an ACL tied to the WLAN so client access can be controlled before and after authentication.
Option D is the only answer that satisfies all requirements: captive portal redirection, post-authentication restriction to Internet-only access, and policy enforcement through ACLs. VLAN-level segmentation is implemented through the WLAN policy profile, which maps guest clients to the guest VLAN rather than the staff VLAN. WPA2-PSK is invalid because the guest SSID must not require a password. A local web server alone does not enforce Internet-only authorization or staff-network isolation. mDNS is unrelated to captive portal authentication or guest segmentation. Reference topics:Guest WLAN design, Central Web Authentication, Catalyst 9800 policy profiles, ACL enforcement, VLAN segmentation, and captive portal client onboarding.
NEW QUESTION # 41
Refer to the exhibit.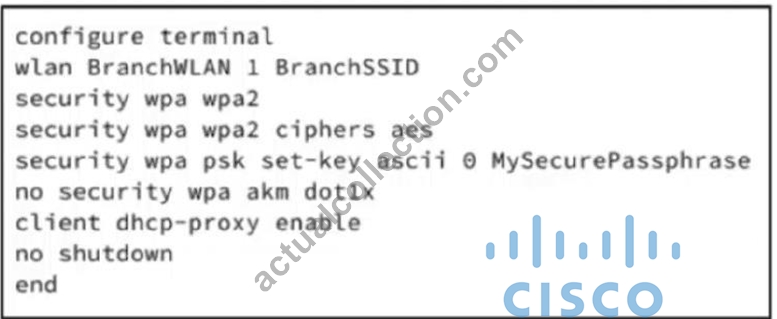
A WLC is deployed at a branch location to facilitate secure client connectivity. A network engineer configures one WLAN using WPA2 Personal passphrase and activates ASCII format key to align with company security policies. Which configuration enables client authentication for this WLAN?
- A. security wpa akm psk set-key ascii 0
- B. client dhcp-proxy enable
- C. no security wpa akm dot1x
- D. security wpa wpa2 ciphers aes
Answer: A
Explanation:
WPA2-Personal authenticates clients with a preshared key, not with 802.1X. Cisco documents WPA/WPA2 as supporting multiple authentication methods, including 802.1X and PSK, and specifically states that when PSK is selected, a preshared key or passphrase must be configured. The configuration element that enables client authentication in this scenario is the PSK ASCII key function represented by option D. On Catalyst
9800 IOS XE, the PSK method is enabled with PSK authentication key management, and the passphrase is defined withsecurity wpa psk set-key {ascii | hex} {0 | 8} password; Cisco's example issecurity wpa psk set- key ascii 0 test.
Option A disables 802.1X AKM, which is appropriate for Personal mode, but it does not by itself authenticate clients. Option B controls DHCP proxy behavior and has no role in WPA authentication. Option C enables AES for WPA2 encryption, which protects traffic confidentiality but does not supply the authentication secret.
Reference topics:Client Connectivity Configuration - WPA2-Personal, PSK authentication, AKM selection, AES encryption, and Catalyst 9800 WLAN security configuration.
NEW QUESTION # 42
Refer to the exhibit. A network engineer must create a PSK WLAN that will be anchored to the DMZ. After this WLAN is created, users cannot connect to it. Based on the output from the RA trace, which action must the engineer take to resolve the issue?
- A. Configure matching WLANs on the foreign and the anchor.
- B. Remove the anchor WLC from the mobility group.
- C. Configure matching passwords on the client and the WLAN.
- D. Disable fast transition 802.11r on the WLAN.
Answer: C
Explanation:
The failure is occurring during WPA/WPA2 key management, not during mobility anchoring. The radioactive trace shows Failed to validate eapol mic. MIC mismatch followed by Failed to validate eapol key m2, which means the authenticator and supplicant derived different key material during the PSK handshake. Cisco's Catalyst 9800 client-connectivity troubleshooting maps this log pattern directly to a wrong password condition and lists the corrective actions as fixing the password on the endpoint or on the SSID/WLAN. The 11r MIC validation failed phrase does not automatically make 802.11r the root cause; it only shows that the failed MIC validation occurred while Fast Transition key logic was in use. Disabling 802.11r would be a workaround only for client capability or FT interoperability issues, but the trace points to PSK mismatch. Removing the anchor WLC would break the intended DMZ anchoring design, and matching WLANs on foreign and anchor is required for anchor deployments, but it would not produce this EAPOL M2 MIC failure. The correct remediation is to ensure the client-entered PSK matches the WLAN PSK.
NEW QUESTION # 43
......
Cisco 350-101 Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
Cisco 350-101 Dumps PDF Are going to be The Best Score: https://www.actualcollection.com/350-101-exam-questions.html
CCIE Wireless 350-101 Exam and Certification Test Engine: https://drive.google.com/open?id=17pmIIslAiKrrpUBQcETsKHoM7ACuT4Qw