

Updated Sep-2026 Test Engine to Practice 200-201 Dumps & Practice Exam
Dumps Collection 200-201 Test Engine Dumps Training With 478 Questions
NEW QUESTION # 253
Which metric in CVSS indicates an attack that takes a destination bank account number and replaces it with a different bank account number?
- A. availability
- B. confidentiality
- C. integrity
- D. scope
Answer: C
NEW QUESTION # 254
Which type of data collection requires the largest amount of storage space?
- A. session data
- B. alert data
- C. transaction data
- D. full packet capture
Answer: D
Explanation:
Full packet capture requires the largest amount of storage space because it involves recording all packets that pass through a network, including all headers and payloads. This type of data collection is comprehensive and allows for detailed analysis, but due to the volume of data it encompasses, it demands significant storage capacity1.
NEW QUESTION # 255
Which system monitors local system operation and local network access for violations of a security policy?
- A. systems-based sandboxing
- B. host-based intrusion detection
- C. host-based firewall
- D. antivirus
Answer: B
Explanation:
Explanation
HIDS is capable of monitoring the internals of a computing system as well as the network packets on its network interfaces. Host-based firewall is a piece of software running on a single Host that can restrict incoming and outgoing Network activity for that host only.
NEW QUESTION # 256
What is the difference between discretionary access control (DAC) and role-based access control (RBAC)?
- A. RBAC access is granted when a user meets specific conditions, and in DAC, permissions are applied on user and group levels.
- B. DAC requires explicit authorization for a given user on a given object, and RBAC requires specific conditions.
- C. RBAC is an extended version of DAC where you can add an extra level of authorization based on time.
- D. DAC administrators pass privileges to users and groups, and in RBAC, permissions are applied to specific groups
Answer: A
Explanation:
In RBAC, access is based on the roles that users have within an organization, and permissions to perform certain operations are assigned to specific roles. DAC, on the other hand, is a type of access control where the access rights are determined by the owner of the resource or the resource itself.
NEW QUESTION # 257
Refer to the exhibit.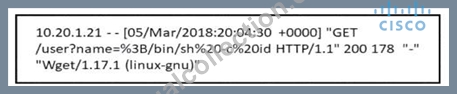
Which attack is being attempted against a web application?
- A. command injection
- B. man-in-the-middle
- C. denial of service
- D. SQL injection
Answer: A
Explanation:
The exhibit shows an HTTP GET request with a parameter that includes; /bin/sh -c id.
This indicates a command injection attempt, where the attacker is trying to execute shell commands on the server.
Command injection vulnerabilities allow an attacker to execute arbitrary commands on the host operating system via a vulnerable application.
The use of/bin/shand the-cflag is typical in command injection exploits to run shell commands, such asid, which returns user identity information.
References
OWASP Command Injection
Analyzing HTTP Requests for Injection Attacks
Web Application Security Testing Guidelines
NEW QUESTION # 258
What is a difference between authorization and authentication from an access control perspective?
- A. Authentication is responsible for accounting access on system resources and the authorization process defines if a user is allowed to author the resource
- B. Authentication is when the system validates if the user is valid, and authorization enforces and provides resources assigned and required.
- C. Authorization tracks if a certain user is authenticated within the system, and authentication is responsible for identifying the authorization method
- D. Authorization defines the author of a specific resource and authentication gives access to the resource itself
Answer: B
NEW QUESTION # 259
Refer to the exhibit.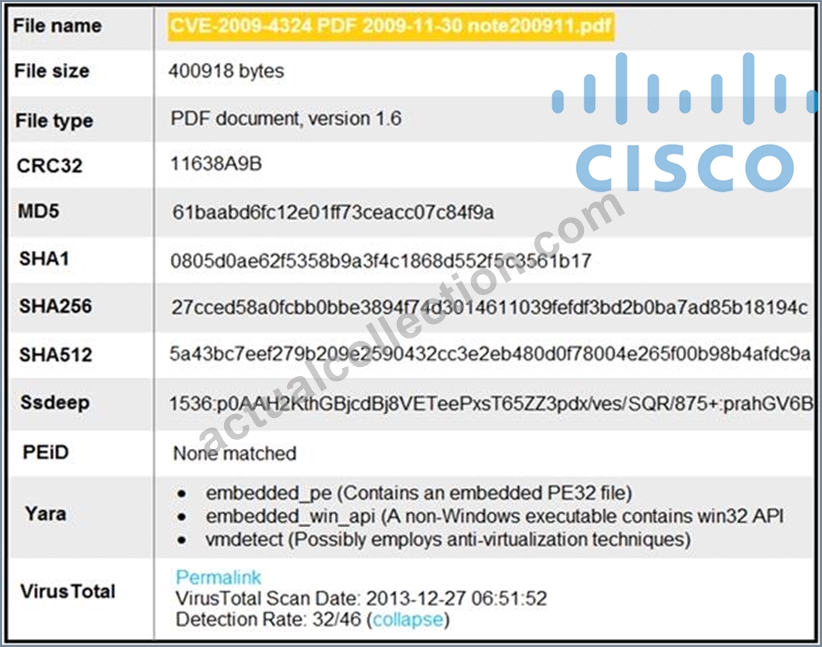
An engineer is analyzing this Cuckoo Sandbox report for a PDF file that has been downloaded from an email. What is the state of this file?
- A. The file has an embedded non-Windows executable but no suspicious features are identified.
- B. The file has an embedded executable and was matched by PEiD threat signatures for further analysis.
- C. The file was matched by PEiD threat signatures but no suspicious features are identified since the signature list is up to date.
- D. The file has an embedded Windows 32 executable and the Yara field lists suspicious features for further analysis.
Answer: D
NEW QUESTION # 260
Refer to the exhibit.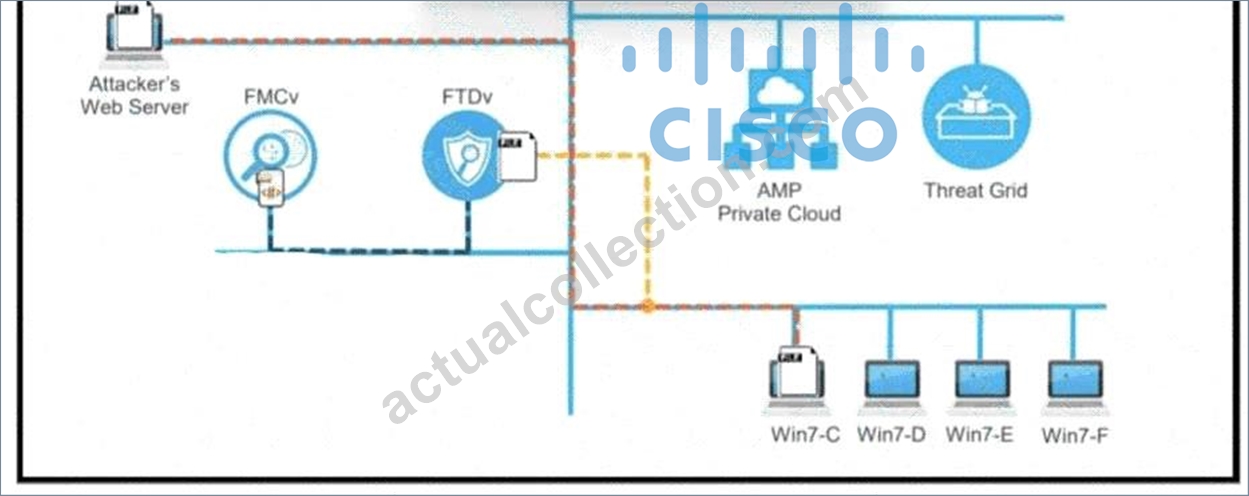
A workstation downloads a malicious docx file from the Internet and a copy is sent to FTDv. The FTDv sends the file hash to FMC and the tile event is recorded what would have occurred with stronger data visibility.
- A. An extra level of security would have been in place
- B. Detailed information about the data in real time would have been provided
- C. Malicious traffic would have been blocked on multiple devices
- D. The traffic would have been monitored at any segment in the network.
Answer: B
Explanation:
With stronger data visibility, detailed information about the data in real-time is provided. This enhanced visibility allows for a more comprehensive analysis of network traffic, enabling security professionals to identify and mitigate threats more effectively. References := Cisco Cybersecurity Operations Fundamentals
NEW QUESTION # 261
Which system monitors local system operation and local network access for violations of a security policy?
- A. systems-based sandboxing
- B. host-based intrusion detection
- C. host-based firewall
- D. antivirus
Answer: B
NEW QUESTION # 262
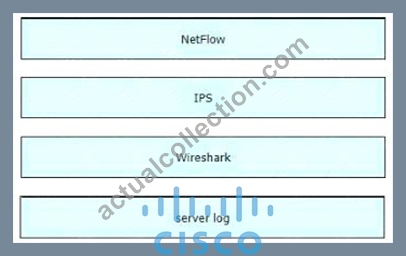
Drag and drop the data source from the left onto the data type on the right.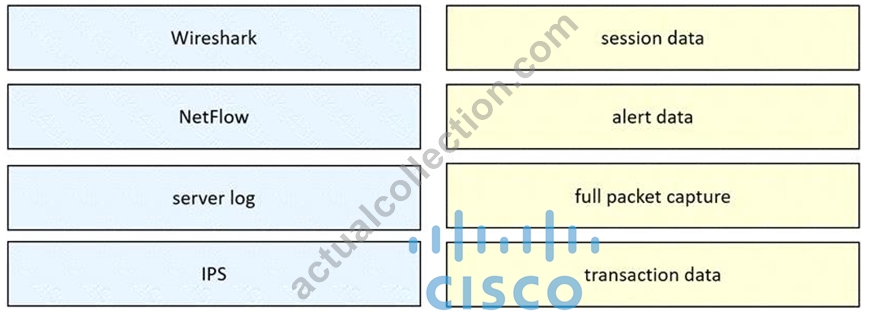
Answer:
Explanation: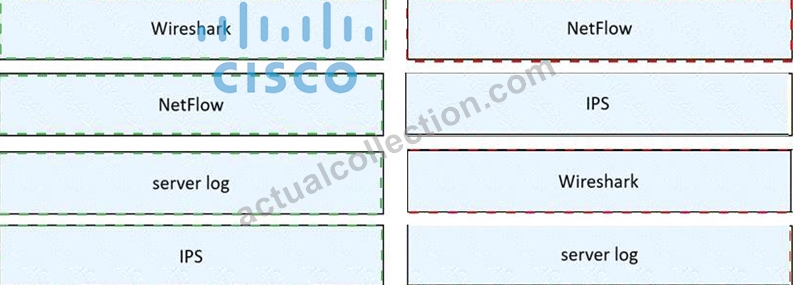
NEW QUESTION # 263
In a SOC environment, what is a vulnerability management metric?
- A. internet exposed devices
- B. code signing enforcement
- C. single factor authentication
- D. full assets scan
Answer: C
NEW QUESTION # 264
What is the difference between indicator of attack (loA) and indicators of compromise (loC)?
- A. loA refers to the individual responsible for the security breach, and loC refers to the resulting loss.
- B. loC is the evidence that a security breach has occurred, and loA allows organizations to act before the vulnerability can be exploited.
- C. loA is the evidence that a security breach has occurred, and loC allows organizations to act before the vulnerability can be exploited.
- D. loC refers to the individual responsible for the security breach, and loA refers to the resulting loss.
Answer: B
Explanation:
Indicators of Compromise (IoC) are pieces of forensic data, such as system log entries or files, that suggest an intrusion may have occurred. Indicators of Attack (IoA) are signs that an attack may be underway, allowing organizations to take action before any potential breach occurs.: The CBROPS course materials cover the concepts of IoC and IoA, explaining how they are used in cybersecurity operations to detect and prevent security incidents.
NEW QUESTION # 265
What causes events on a Windows system to show Event Code 4625 in the log messages?
- A. The system detected an XSS attack
- B. Another device is gaining root access to the system
- C. A privileged user successfully logged into the system
- D. Someone is trying a brute force attack on the network
Answer: D
Explanation:
Event Code 4625 in Windows logs indicates a failed logon attempt. This could be a sign of someone trying to guess the credentials of a valid user account by repeatedly trying different passwords or usernames. This is known as a brute force attack and can be used to gain unauthorized access to a system or network. Reference: https://www.cisco.com/c/en/us/td/docs/security/ise/2-4/admin_guide/b_ise_admin_guide_24/b_ise_admin_guide_24_new_chapter_01110.html
NEW QUESTION # 266
Why is encryption challenging to security monitoring?
- A. Encryption analysis is used by attackers to monitor VPN tunnels.
- B. Encryption introduces larger packet sizes to analyze and store.
- C. Encryption is used by threat actors as a method of evasion and obfuscation.
- D. Encryption introduces additional processing requirements by the CPU.
Answer: C
Explanation:
Encryption is challenging to security monitoring because it can be used by threat actors as a method of evasion and obfuscation. Encryption can prevent security devices from inspecting the content or payload of the network traffic, making it difficult to detect malicious activity or signatures. Encryption can also hide the source and destination of the traffic, making it hard to trace the origin or destination of the attack. Reference: https://learningnetworkstore.cisco.com/on-demand-e-learning/understanding-cisco-cybersecurity-operations-fundamentals-cbrops-v1-0/CSCU-LP-CBROPS-V1-028093.html (Module 4, Lesson 4.1.1)
NEW QUESTION # 267 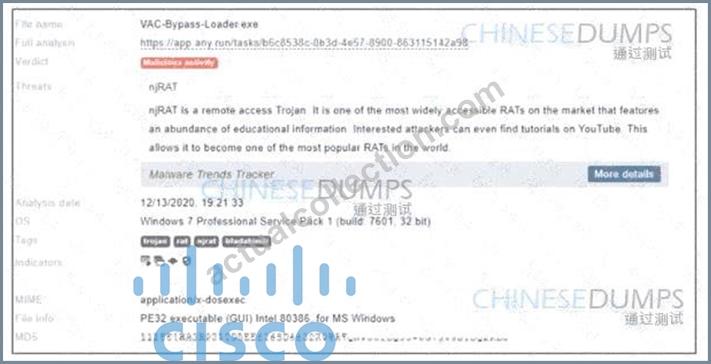
Refer to the exhibit. Where is the executable file?
- A. info
- B. MIME
- C. tags
- D. name
Answer: D
Explanation:
The executable file is identified in the "name" section of the exhibit, which lists the file name "VAC-Bypass- Loader.exe". This indicates that the file is an executable, as denoted by the ".exe" extension commonly associated with executable files in Windows operating systems.
The information provided is based on standard practices for identifying executable files within cybersecurity analysis reports and is consistent with Cisco's cybersecurity documentation.
NEW QUESTION # 268
What is the purpose of a host-based intrusion detection system (HIDS)?
- A. A HIDS filters traffic according to configured firewall access control rules.
- B. A HIDS detects threats using a combination of signature-based and anomaly-based detection methods.
- C. A HIDS protects against threats via known denylisted hash databases of malware and ransomware.
- D. A HIDS blocks potential anomalous user activity.
Answer: B
Explanation:
A host-based intrusion detection system (HIDS) is designed to detect malicious activity on individual hosts by monitoring system behavior, logs, file integrity, and processes. Unlike firewalls or antivirus tools, a HIDS focuses on detecting suspicious or unauthorized activity rather than blocking traffic or enforcing access rules.
HIDS solutions typically use a combination of signature-based detection, which identifies known attack patterns, and anomaly-based detection, which identifies deviations from normal system behavior. This dual approach allows a HIDS to detect both known threats and previously unseen attacks.
Option A describes antivirus functionality rather than intrusion detection. Option B refers to firewall behavior, which is network-focused, not host-based. Option D describes intrusion prevention, not detection.
Cybersecurity operations fundamentals clearly distinguish HIDS as a detection technology, often paired with host-based intrusion prevention systems (HIPS) for blocking capabilities.
Therefore, the purpose of a HIDS is to detect threats using both signature-based and anomaly-based techniques, making Option C the correct answer.
NEW QUESTION # 269
Refer to the exhibit.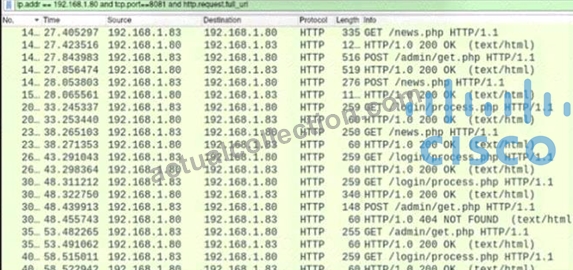
A network administrator is investigating suspicious network activity by analyzing captured traffic. An engineer notices abnormal behavior and discovers that the default user agent is present in the headers of requests and data being transmitted What is occurring?
- A. garbage flood attack attacker is sending garbage binary data to open ports
- B. indicators of data exfiltration HTTP requests must be plain text
- C. cache bypassing attack: attacker is sending requests for noncacheable content
- D. indicators of denial-of-service attack due to the frequency of requests
Answer: C
Explanation:
The presence of a default user agent in the headers of requests and data being transmitted suggests a cache bypassing attack. In this scenario, the attacker is likely requesting noncacheable content to avoid detection by caching mechanisms that could otherwise identify and block malicious traffic.
NEW QUESTION # 270
Which tool provides a full packet capture from network traffic?
- A. Hydra
- B. Wireshark
- C. Nagios
- D. CAINE
Answer: B
NEW QUESTION # 271
......
Cisco 200-201 Dumps Cover Real Exam Questions: https://www.actualcollection.com/200-201-exam-questions.html
Real 200-201 dumps - Real Cisco dumps PDF: https://drive.google.com/open?id=18C8ABf-CmwTQD3-ptNU-TpWzRzkprhFQ