

New (2021) Cisco 350-401 Exam Dumps
Best Way To Study For Cisco 350-401 Exam Brilliant 350-401 Exam Questions PDF
As infrastructure, networking, and software grow more interconnected every day, the IT specialists have to prove their positions in the constantly evolving environment of networking technologies. That is why they take the exams to obtain the certifications that will validate their skills. Thus, Cisco offers to earn the CCIE Enterprise Infrastructure, CCIE Enterprise Wireless, and CCNP Enterprise certificates, which will demonstrate that the professionals possess the knowledge of securing and scaling the networking infrastructure.
To get these certifications, the applicants should start with passing the core exam, which is Cisco 350-401 ENCOR. After that, they will have to sit for the practical lab test (for CCIE Enterprise Infrastructure & CCIE Enterprise Wireless) or one of the concentration exams of your choice (there are 6 of them for CCNP Enterprise).
NEW QUESTION 108
Drag and drop the characteristic from the left onto the orchestration tools that they describe on the right.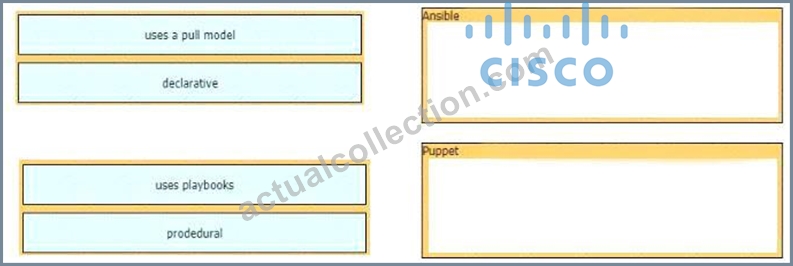
Answer:
Explanation: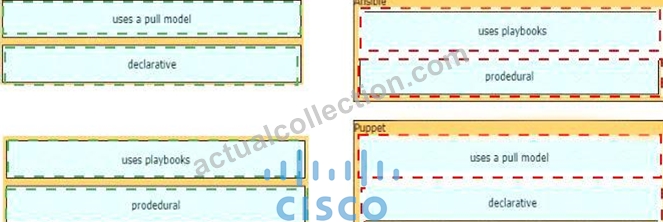
Explanation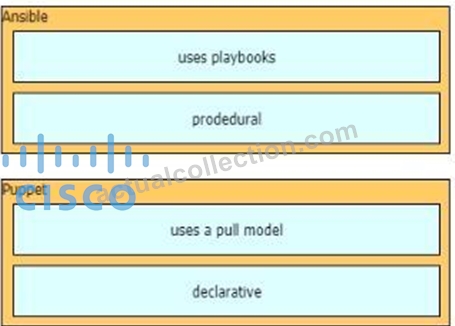
NEW QUESTION 109
Refer to the exhibit.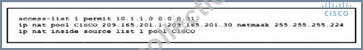
What are two effect of this configuration? (Choose two.)
- A. The 10.1.1.0/27 subnet is assigned as the inside global address range.
- B. It establishes a one-to-one NAT translation.
- C. Inside source addresses are translated to the 209.165.201.0/27 subnet.
- D. The 10.1.1.0/27 subnet is assigned as the inside local addresses.
- E. The 209.165.201.0/27 subnet is assigned as the outside local address range.
Answer: C,D
NEW QUESTION 110
What does this EEM applet event accomplish?
"event snmp oid 1.3.6.1.3.7.1.5.1.2.4.2.9 get-type next entry-op g entry-val 75 poll-interval 5"
- A. Upon the value reaching 75%, a SNMP event is generated and sent to the trap server.
- B. It reads an SNMP variable, and when the value exceeds 75% for live polling cycles.
- C. It presents a SNMP variable that can be interrogated.
- D. It issues email when the value is greater than 75% for five polling cycles.
Answer: B
Explanation:
Explanation
EEM offers the ability to monitor events and take informational or corrective action when the monitored events occur or reach a threshold. An EEM policy is an entity that defines an event and the actions to be taken when that event occurs. There are two types of EEM policies: an applet or a script. An applet is a simple form of policy that is defined within the CLI configuration.
To specify the event criteria for an Embedded Event Manager (EEM) applet that is run by sampling Simple Network Management Protocol (SNMP) object identifier values, use the event snmp command in applet configuration mode.
event snmp oid oid-value get-type {exact | next} entry-op operator entry-val entryvalue
[exit-comb {or | and}] [exit-op operator] [exit-val exit-value] [exit-time exit-timevalue] poll-interval poll-int-value
+ oid: Specifies the SNMP object identifier (object ID)
+ get-type: Specifies the type of SNMP get operation to be applied to the object ID specified by the oid-value argument.
- next - Retrieves the object ID that is the alphanumeric successor to the object ID specified by the oid-value argument.
+ entry-op: Compares the contents of the current object ID with the entry value using the specified operator. If there is a match, an event is triggered and event monitoring is disabled until the exit criteria are met.
+ entry-val: Specifies the value with which the contents of the current object ID are compared to decide if an SNMP event should be raised.
+ exit-op: Compares the contents of the current object ID with the exit value using the specified operator. If there is a match, an event is triggered and event monitoring is reenabled.
+ poll-interval: Specifies the time interval between consecutive polls (in seconds) Reference: https://www.cisco.com/en/US/docs/ios/12_3t/12_3t4/feature/guide/gtioseem.html Question 2 Cisco TrustSec uses tags to represent logical group privilege. This tag, called a Security Group Tag (SGT), is used in access policies. The SGT is understood and is used to enforce traffic by Cisco switches, routers and firewalls . Cisco TrustSec is defined in three phases: classification, propagation and enforcement.
When users and devices connect to a network, the network assigns a specific security group. This process is called classification. Classification can be based on the results of the authentication or by associating the SGT with an IP, VLAN, or port-profile (-> Answer 'security group tag ACL assigned to each port on a switch' and answer 'security group tag number assigned to each user on a switch' are not correct as they say "assigned ... on a switch" only. Answer 'security group tag ACL assigned to each router on a network' is not correct either as it says "assigned to each router").
NEW QUESTION 111
Refer to the exhibit. An engineer is configuring an EtherChannel between Switch1 and Switch2 and notices the console message on switch2. Based on the output, which action resolves this issue?
- A. Configure more member ports on Switch1.
- B. Configure the same port channel interface number on both switches
- C. Configure less member ports on Switch2.
- D. Configure the same EtherChannel protocol on both switches
Answer: D
Explanation:
In this case, we are using your EtherChannel without a negotiation protocol on Switch2. As a result, if the opposite switch is not also configured for EtherChannel operation on the respective ports, there is a danger of a switching loop. The EtherChannel Misconfiguration Guard tries to prevent that loop from occuring by disabling all the ports bundled in the EtherChannel.
NEW QUESTION 112
Drag and drop the LIPS components on the left to the correct description on the right.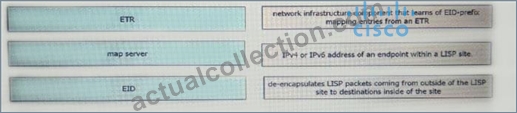
Answer:
Explanation: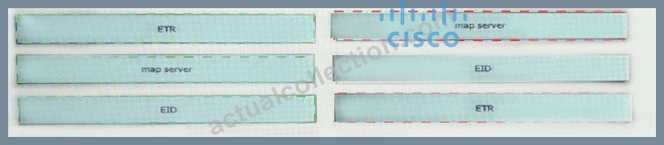
* Map server
* EID
* ETR
NEW QUESTION 113
An engineer creates the configuration below. Drag and drop the authentication methods from the left into the order of priority on the right. Not all options are used.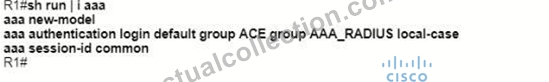
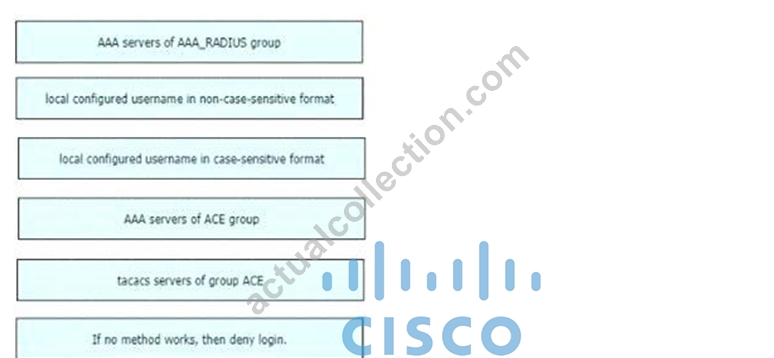
Answer:
Explanation: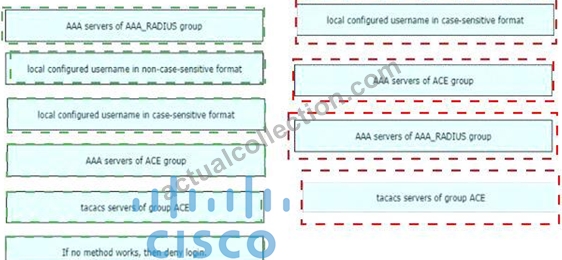
Explanation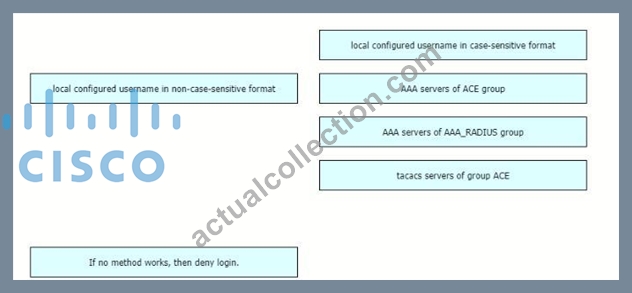
NEW QUESTION 114
Refer to Exhibit.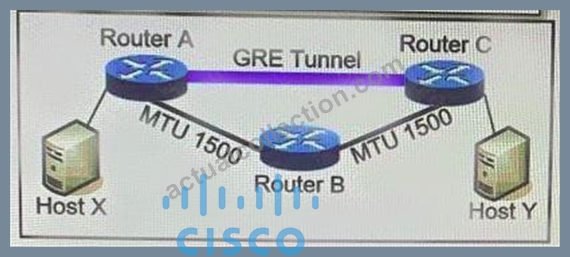
MTU has been configured on the underlying physical topology, and no MTU command has been configured on the tunnel interfaces. What happens when a 1500-byte IPv4 packet traverses the GRE tunnel from host X to host Y, assuming the DF bit is cleared?
- A. The packet is discarded on router B
- B. The packet arrives on router C without fragmentation.
- C. The packet arrives on router C fragmented.
- D. The packet is discarded on router A
Answer: C
Explanation: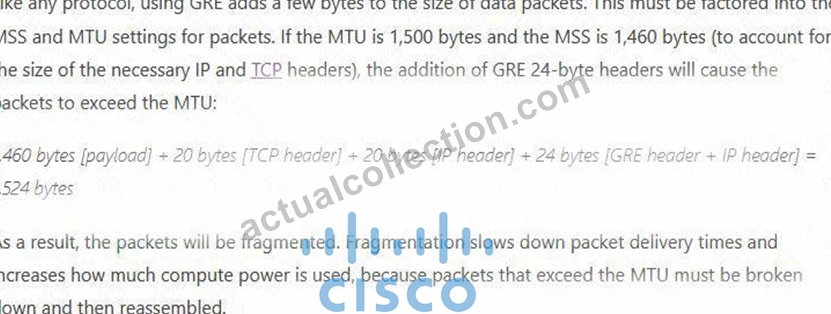
NEW QUESTION 115
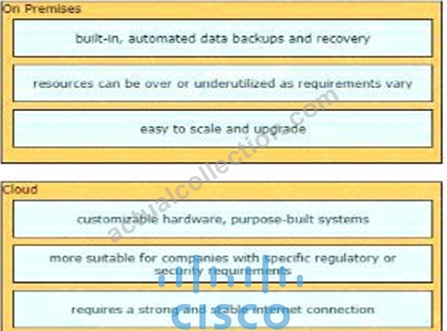
Drag and drop the characteristics from the left onto the correct infrastructure deployment types on the right.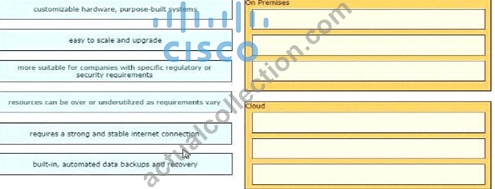
Answer:
Explanation: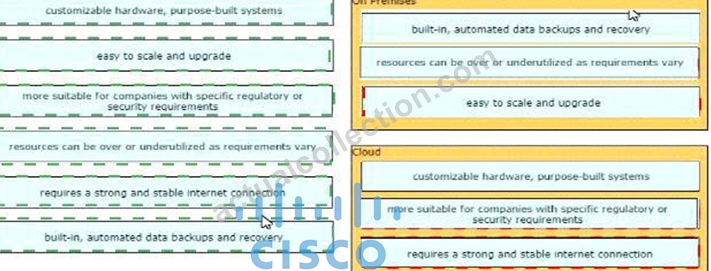
NEW QUESTION 116
What is the function of the fabric control plane node In a Cisco SD-Access deployment?
- A. It is responsible for policy application and network segmentation in the fabric.
- B. It performs traffic encapsulation and security profiles enforcement in the fabric.
- C. It provides Integration with legacy nonfabric-enabled environments.
- D. It holds a comprehensive database that tracks endpoints and networks in the fabric.
Answer: D
Explanation:
Reference:
Fabric control plane node (C): One or more network elements that implement the LISP Map-Server (MS) and Map-Resolver (MR) functionality. The control plane node's host tracking database keep track of all endpoints in a fabric site and associates the endpoints to fabric nodes in what is known as an EID-to-RLOC binding in LISP.
NEW QUESTION 117
Drag and drop the LISP components from the left onto the function they perform on the right. Not all options are used.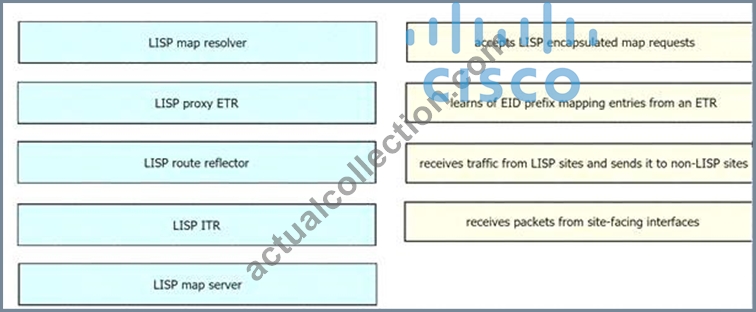
Answer:
Explanation: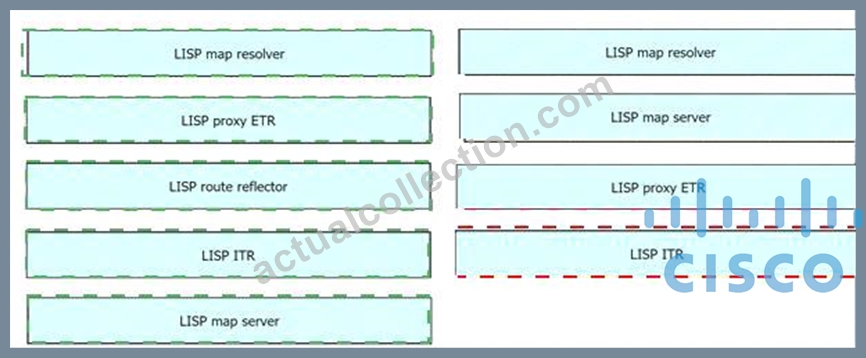
Explanation
Table Description automatically generated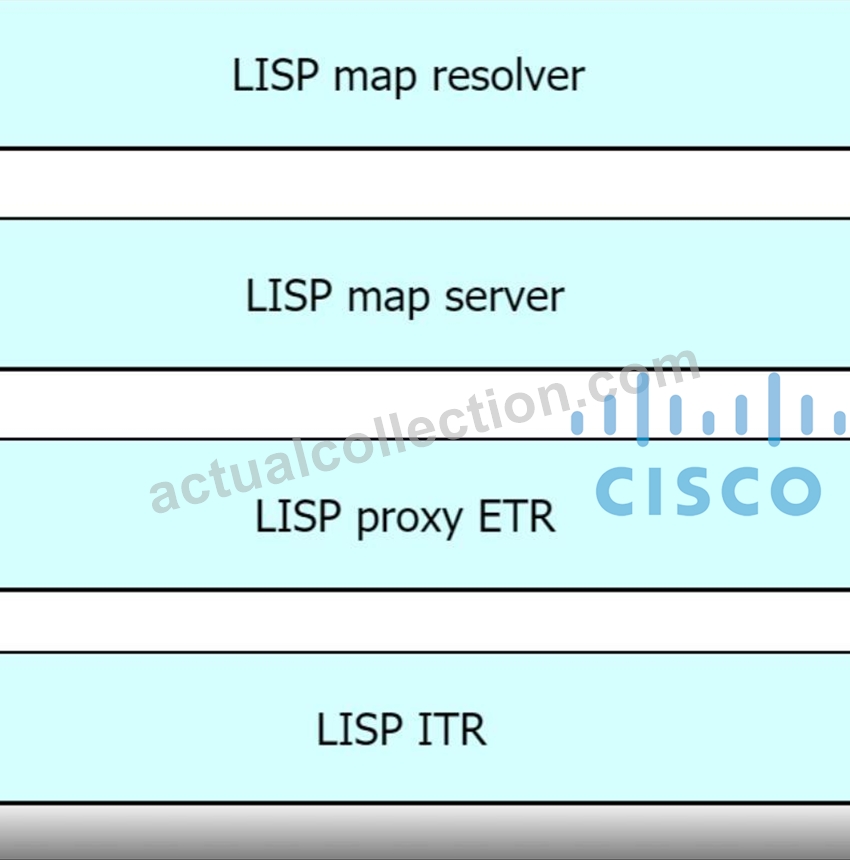
+ accepts LISP encapsulated map requests: LISP map resolver
+ learns of EID prefix mapping entries from an ETR: LISP map server
+ receives traffic from LISP sites and sends it to non-LISP sites: LISP proxy ETR
+ receives packets from site-facing interfaces: LISP ITR
Explanation
ITR is the function that maps the destination EID to a destination RLOC and then encapsulates the original packet with an additional header that has the source IP address of the ITR RLOC and the destination IP address of the RLOC of an Egress Tunnel Router (ETR).
After the encapsulation, the original packet become a LISP packet.
ETR is the function that receives LISP encapsulated packets, decapsulates them and forwards to its local EIDs. This function also requires EID-to-RLOC mappings so we need to point out an "map-server" IP address and the key (password) for authentication.
A LISP proxy ETR (PETR) implements ETR functions on behalf of non-LISP sites. A PETR is typically used when a LISP site needs to send traffic to non-LISP sites but the LISP site is connected through a service provider that does not accept no routable EIDs as packet sources. PETRs act just like ETRs but for EIDs that send traffic to destinations at non-LISP sites.
Map Server (MS) processes the registration of authentication keys and EID-to-RLOC mappings. ETRs sends periodic Map-Register messages to all its configured Map Servers.
Map Resolver (MR): a LISP component which accepts LISP Encapsulated Map Requests, typically from an ITR, quickly determines whether or not the destination IP address is part of the EID namespace
NEW QUESTION 118
Which statement about a fabric access point is true?
- A. It is in local mode an must be connected directly to the fabric border node.
- B. It is in FlexConnect mode and must be connected directly to the fabric edge switch.
- C. It is in FlexConnect mode and must be connected directly to the fabric border node.
- D. It is in local mode an must connected directly to the fabric edge switch.
Answer: D
Explanation:
Explanation
Fabric mode APs continue to support the same wireless media services that traditional APs support; apply AVC, quality of service (QoS), and other wireless policies; and establish the CAPWAP control plane to the fabric WLC. Fabric APs join as local-mode APs and must be directly connected to the fabric edge node switch to enable fabric registration events, including RLOC assignment via the fabric WLC. The fabric edge nodes use CDP to recognize APs as special wired hosts, applying special port configurations and assigning the APs to a unique overlay network within a common EID space across a fabric. The assignment allows management simplification by using a single subnet to cover the AP infrastructure at a fabric site.
Reference: https://www.cisco.com/c/en/us/td/docs/solutions/CVD/Campus/sda-sdg-2019oct.html
NEW QUESTION 119
Which two operations are valid for RESTCONF? (Choose two.)
- A. ADD
- B. PUSH
- C. PULL
- D. REMOVE
- E. PATCH
- F. HEAD
Answer: D,E
NEW QUESTION 120
Drag and drop the Qos mechanisms from the left to the correct descriptions on the right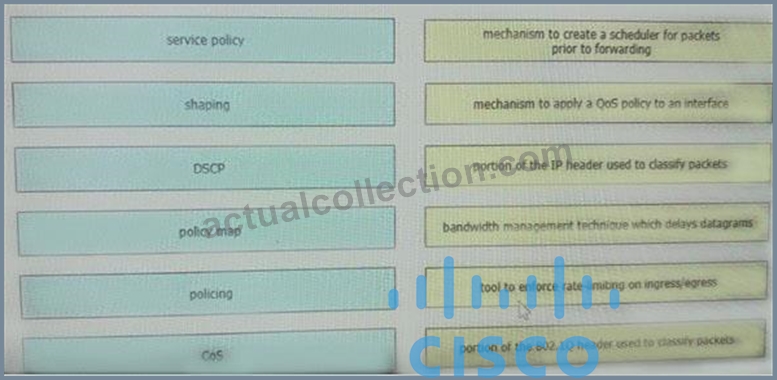
Answer:
Explanation: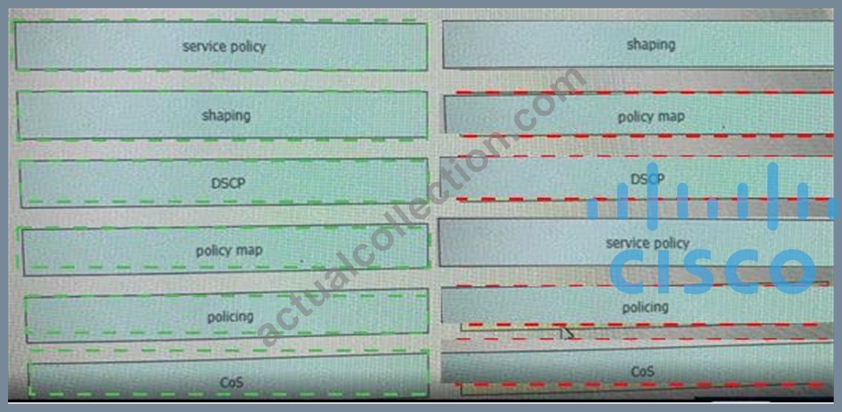
Explanation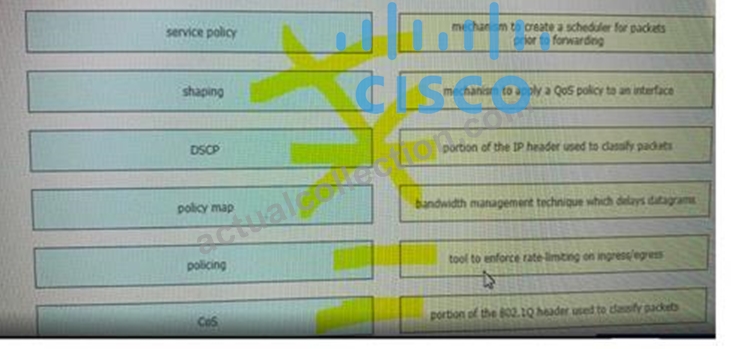
NEW QUESTION 121
Which feature must be configured to allow packet capture over Layer 3 infrastructure'?
- A. IPSPAN
- B. ERSPAN
- C. RSPAN
- D. VSPAN
Answer: B
Explanation:
Reference:
Encapsulated remote SPAN (ERSPAN): encapsulated Remote SPAN (ERSPAN), as the name says, brings generic routing encapsulation (GRE) for all captured traffic and allows it to be extended across Layer 3 domains.
NEW QUESTION 122
A network administrator applies the following configuration to an IOS device.
What is the process of password checks when a login attempt is made to the device?
- A. A TACACS+server is checked first. If that check fail, a RADIUS server is checked. If that check fail. a local database is checked.
- B. A TACACS+server is checked first. If that check fail, a database is checked?
- C. A local database is checked first. If that check fails, a TACACS+server is checked.
- D. A local database is checked first. If that fails, a TACACS+server is checked, if that check fails, a RADUIS server is checked.
Answer: C
Explanation:
Explanation
The "aaa authentication login default local group tacacs+" command is broken down as follows:
+ The 'aaa authentication' part is simply saying we want to configure authentication settings.
+ The 'login' is stating that we want to prompt for a username/password when a connection is made to the device.
+ The 'default' means we want to apply for all login connections (such as tty, vty, console and aux). If we use this keyword, we don't need to configure anything else under tty, vty and aux lines. If we don't use this keyword then we have to specify which line(s) we want to apply the authentication feature.
+ The 'local group tacacs+" means all users are authenticated using router's local database (the first method). If the credentials are not found on the local database, then the TACACS+ server is used (the second method).
NEW QUESTION 123
Drag the drop the description from the left onto the routing protocol they describe on the right.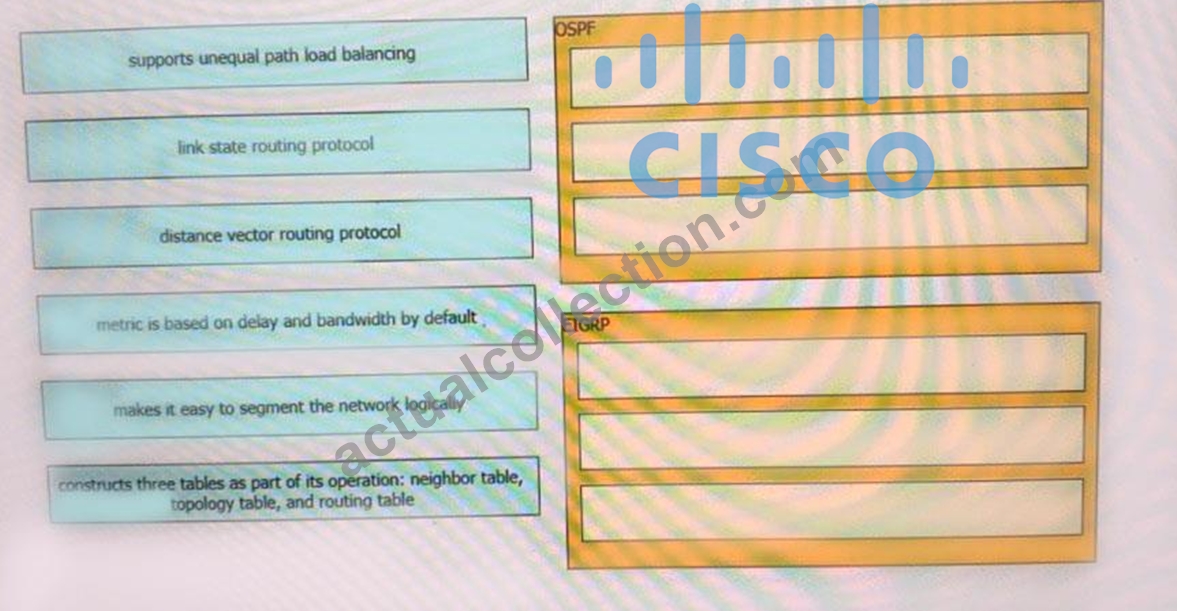
Answer:
Explanation: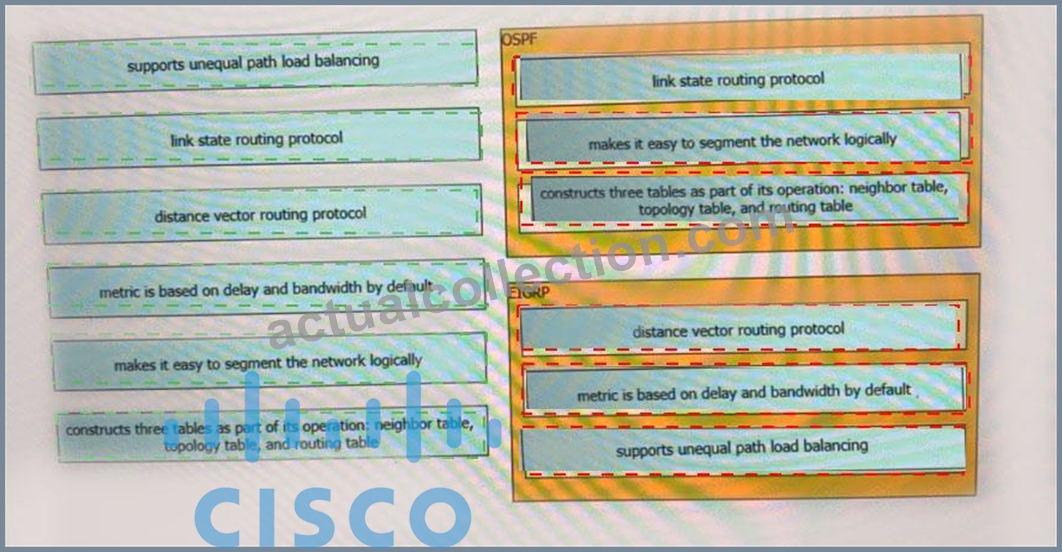
Explanation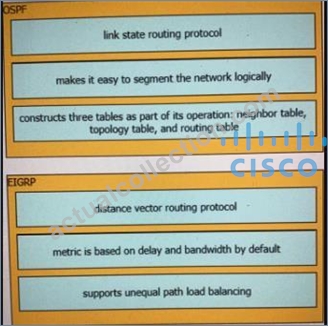
NEW QUESTION 124
Drag and drop the characteristics from the left onto the routing protocols they describe on the right.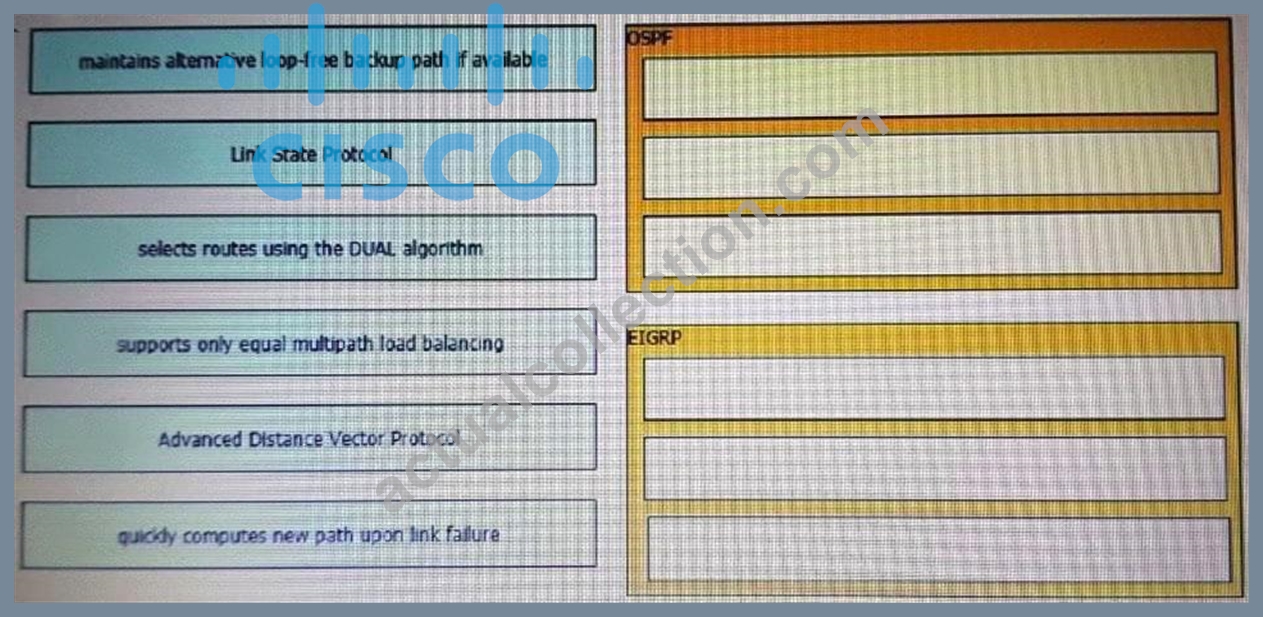
Answer:
Explanation: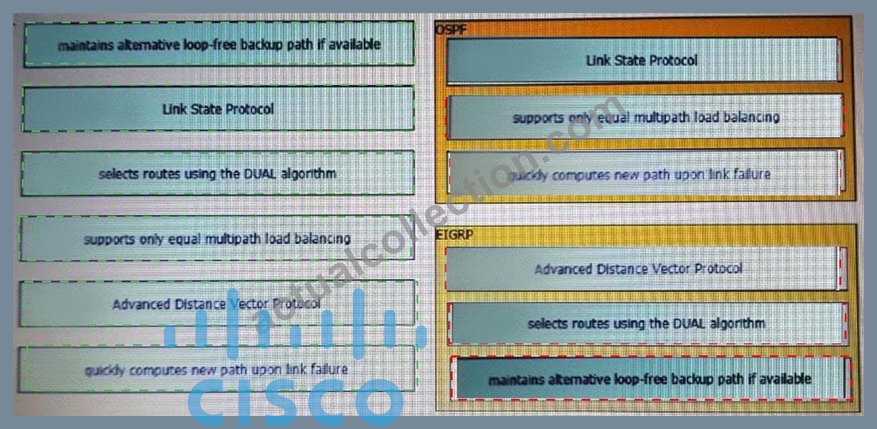
Explanation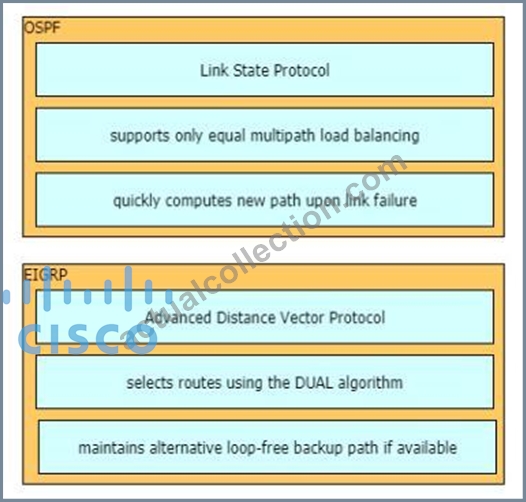
EIGRP maintains alternative loop-free backup via the feasible successors. To qualify as a feasible successor, a router must have an Advertised Distance (AD) less than the Feasible distance (FD) of the current successor route.
Advertised distance (AD): the cost from the neighbor to the destination. Feasible distance (FD): The sum of the AD plus the cost between the local router and the next-hop router
NEW QUESTION 125
Which element enables communication between guest VMs within a virtualized environment?
- A. virtual router
- B. hypervisor
- C. pNIC
- D. vSwitch
Answer: D
Explanation:
Each VM is provided with a virtual NIC (vNIC) that is connected to the virtual switch. Multiple vNICs can connect to a single vSwitch, allowing VMs on a physical host to communicate with one another at layer 2 without having to go out to a physical switch.
NEW QUESTION 126
How does SSO work with HSRP to minimize network disruptions?
- A. It enables HSRP to failover to the standby RP on the same device.
- B. It enables data forwarding along known routes following a switchover, white the routing protocol reconverges.
- C. It enables HSRP to elect another switch in the group as the active HSRP switch.
- D. It ensures fast failover in the case of link failure.
Answer: A
Explanation:
NEW QUESTION 127
......
Related Certification: CCNP Enterprise
Enterprise networking continues to witness massive growth ever since Cisco introduced a new certification curriculum in early 2020. This is best shown by the increasing popularity of the Cisco CCNP Enterprise certification, which does much more than just equipping you with vital IT skills. The new CCNP Enterprise training embodies success with enterprise networking technologies and to obtain it, you must pass two exams: the aforementioned Cisco 350-401, which is a core validation, and one additional concentration exam. That being said, the full list of the concentration tests associated with this learning path includes 300-410, 300-415, 300-420, 300-425, 300-430, and 300-435 exams.
Updated Verified Pass 350-401 Exam - Real Questions & Answers: https://www.actualcollection.com/350-401-exam-questions.html
Dumps Moneyack Guarantee - 350-401 Dumps Approved Dumps: https://drive.google.com/open?id=1WuaLyg8y4SiKZuv_PW9nnD8mYV9Ba2im